What Tessera stores
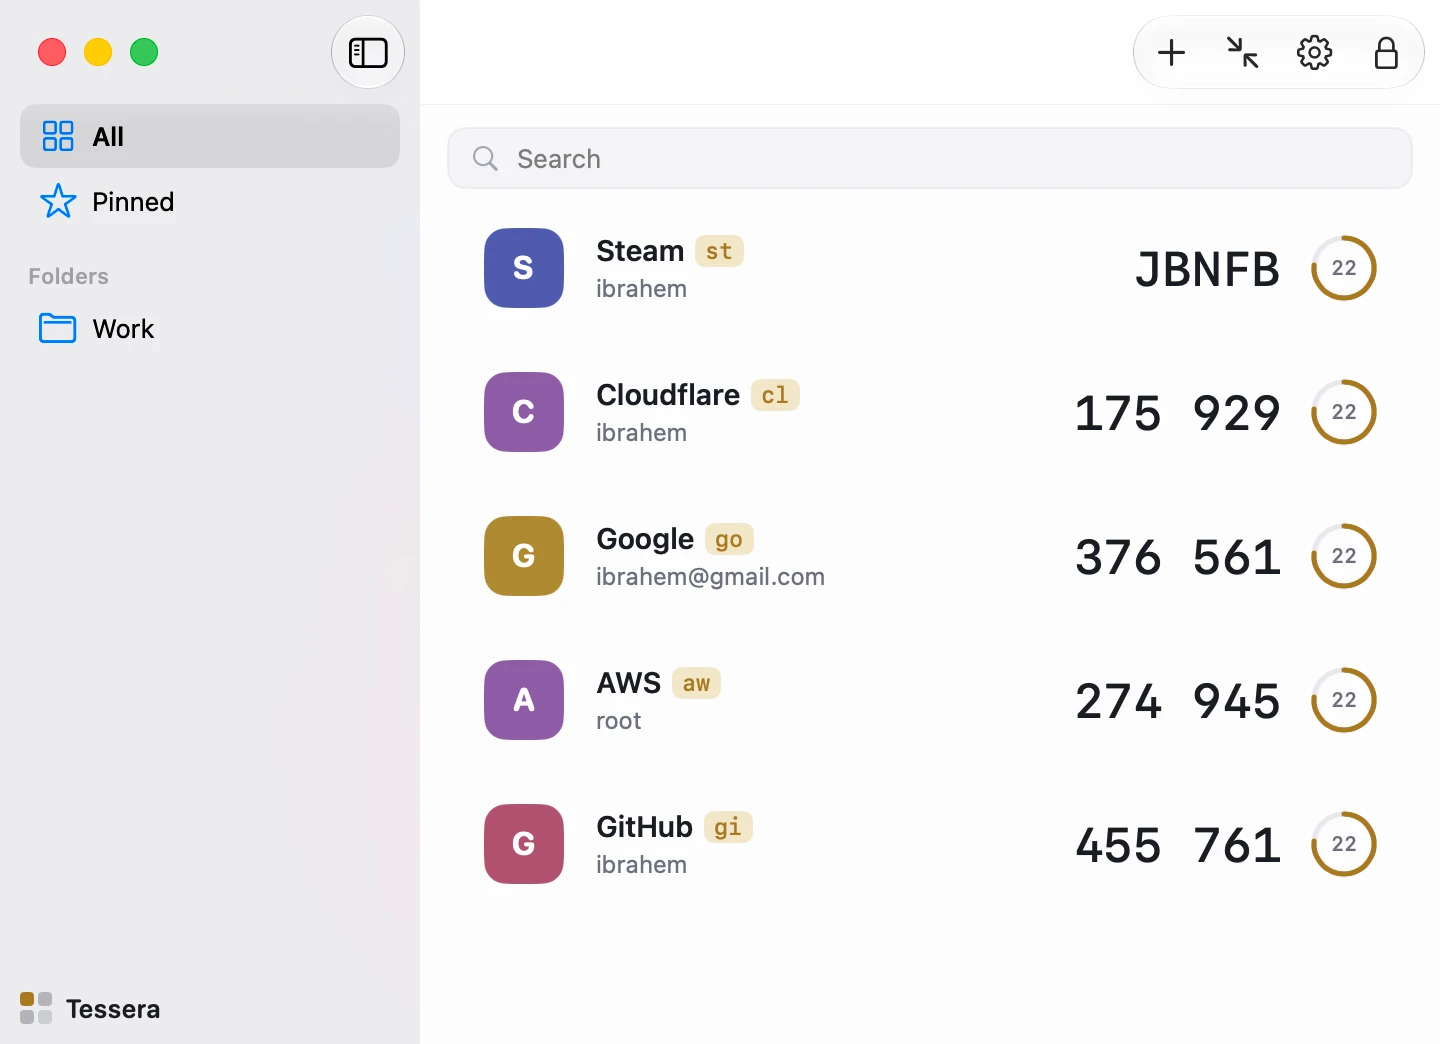
Your two-factor accounts (issuer, label, and secret keys) are kept in an encrypted vault on your Mac. The vault is sealed with XChaCha20-Poly1305 under a random key. That key is wrapped independently by each unlock method: the Secure Enclave on a Mac, and an argon2id key derived from your passphrase. Touch ID can gate the Secure Enclave wrap.
What Tessera transmits
Nothing. Codes are generated offline. Tessera connects to no server we operate and contains no analytics, advertising, or crash-reporting SDKs. The app has no network entitlement.
Permissions
Tessera runs in the macOS App Sandbox. On-screen QR scanning asks macOS for Screen Recording permission, used only to read a QR code at the moment you trigger a scan. Importing a file asks you to pick that file. Tessera requests no other permissions. Auto-launch, when you enable it, registers Tessera as a macOS login item.
Data collection
Tessera collects no data, as Apple's App Privacy guidelines define it. We cannot see your accounts or your codes. The Mac App Store privacy label reads Data Not Collected.
This website
Page views are counted with a self-hosted Umami instance at stats.ibrahemid.com. It sets no cookies, stores no IP addresses, and shares nothing with third parties.
Open source
Tessera is open source under Apache-2.0. You can read exactly what it does and build it yourself: github.com/ibrahemid/tessera. The security details are on /security.
Contact
Questions about privacy: support@ibrahemid.com.